You probably don’t give much thought to the smart functionality of ovens, washers, TV boxes. But Anthropic has—and it believes such IoT devices are ripe for AI exploitation.
How? Self-replicating “AI worms.”
Welcome to Safe Mode, your weekly report for pressing security and privacy news—and what steps to take next. Want this newsletter to come directly to your inbox? Sign up on our website!
Last week, Anthropic released a report detailing a series of experiments—tasking AI with spreading itself across low-tech smart machines. The team examined how easily small models could discover, configure, and install model weights (that is, the model’s parameters for data processing) on vulnerable devices, then repeat the process to proliferate. The resulting botnet (and collective compute power) could then be used for AI workloads. The behavior mirrors that of a classic computer worm, where zero human oversight is needed for the malicious code to copy continuously.
(What’s a small model? AI comes in different sizes, so to speak. The ones we consumers best know represent the large-language variety, like Claude, ChatGPT, Gemini, etc. But small-language versions exist, too. They’re more streamlined and generally built for specific purposes. Think of an LLM as a sprawling multipurpose tool, while an SLM is a single-purpose one. And sometimes a very singular purpose at that.)
Turns out, small, specialized AI models achieved this goal pretty effectively. At least, they did so in a controlled lab environment, with researchers unleashing several small models on Android TV boxes. (Such media boxes have notoriously lax security configurations.) But Anthropic believes this attack method could become real “within months.”
Sounds scary, right? I have to admit that when I first saw a news headline about this report, it felt appropriately spooky for October. After all, we already know the overwhelming majority of smart devices have poor security. (Heck, I’ve written about the very topic, and multiple times at that.) Botnets have also been around forever. The idea of them becoming more advanced through AI isn’t a shocker, either. But I read the report more as a heads-up than a dire warning.
Nicolas J Leclercq / Unsplash
First: Anthropic came to these results in a controlled environment, rather than seeing it on the open internet. (Shenanigans in the wild are the province of its large-language models at the moment.)
Second: Anthropic’s predictions for when we’d see this in the wild is fairly vague. Sure, the implication is just a handful of months, based on current rates of AI improvement. But “months” is very open.
Third: The speed of such attacks is relatively slow. On the LLM side, security professionals talk about vulnerabilities and subsequent exploits happening within hours, if not minutes. But for small AI to proliferate in this way, Anthropic noted times of 10 to 30 hours for spread. Getting the AI models fully operational on the newly infected devices ranged between 28-71 hours at minimum and around 51 to 150 hours maximum, depending on the model.
Cybersecurity defenders thus have more time to quarantine infected devices—and for this particular kind of attack, bad actors have a disincentive to go faster. Spreading quicker makes detection easier.
Fourth: Use of connected devices with higher performing hardware appears to be more difficult—their configurations aren’t as simple (or slapdash) as with cheap internet products.
Finally, even if hackers start using small AI like this,we as consumers still can take some steps to strengthen our device security. We already know the steps: Keep devices off the internet if you’re not using them as connected devices. Change default passwords to something random, unique, and strong. Isolate the devices on their own subnetwork when feasible.
Of course, none of these points are fixed. Bad actors could still choose speed over stealth. They could figure out how to take over devices like smart cameras, drones, and vehicles. But even as AI makes tech more complex, not all protective measures have to be equally so.
In the news
I just spent the last week at TechCrunch Disrupt, listening to multiple presentations about AI and cybersecurity. But even the most interesting thoughts for the future couldn’t tear my attention away from current events.
The dangers we have to watch out for now? More calendar invite scams, compromised Android phones, additional reminders to keep Windows updated, and yet more data breaches.
The painful
- I talked last week about password simplicity—and the need to pair it with password strength. And then a hacker claimed a breach of the Danish national registry came about because the password “123456” worked. Please change your weak passwords, folks.
The annoying
- See an unfamiliar meeting on your calendar? Don’t click on any links embedded in its description. You may get jumped to a phishing site, meant to steal your login info. Delete the invite or report it as junk. (Responding may alert the attacker that the email address is valid and active.)
- Your Windows 11 machine may stop getting updates in spring 2027—if the version you’re on is too old. Microsoft says certificates that enable automatic updates are expiring, and only newer versions of Windows 11 will get the current versions pushed to them. You should be on 26H2 or 25H2 for a seamless transition.
The concerning
- Attackers hacked into refrigerators at French supermarkets and turned up the temperature overnight, causing food spoilage and financial losses. Cybersecurity has been a low priority for many industries, but that may have to change as mundane elements from our daily lives get targeted.
The ugly
- Shop at ASOS? Your customer data may have been stolen after a successful social engineering attack on the company. Data lost includes full names, contact information, and “non-personal account-related information,” according to BleepingComputer. Be wary about any messages related to your ASOS account in the coming weeks.
- A cheap Android phone could land in your hands compromised. Researchers at Bitdefender have discovered embedded malware in low-cost phones with MediaTek chips, likely installed somewhere between device production and arrival on retail shelves.
Tip of the week
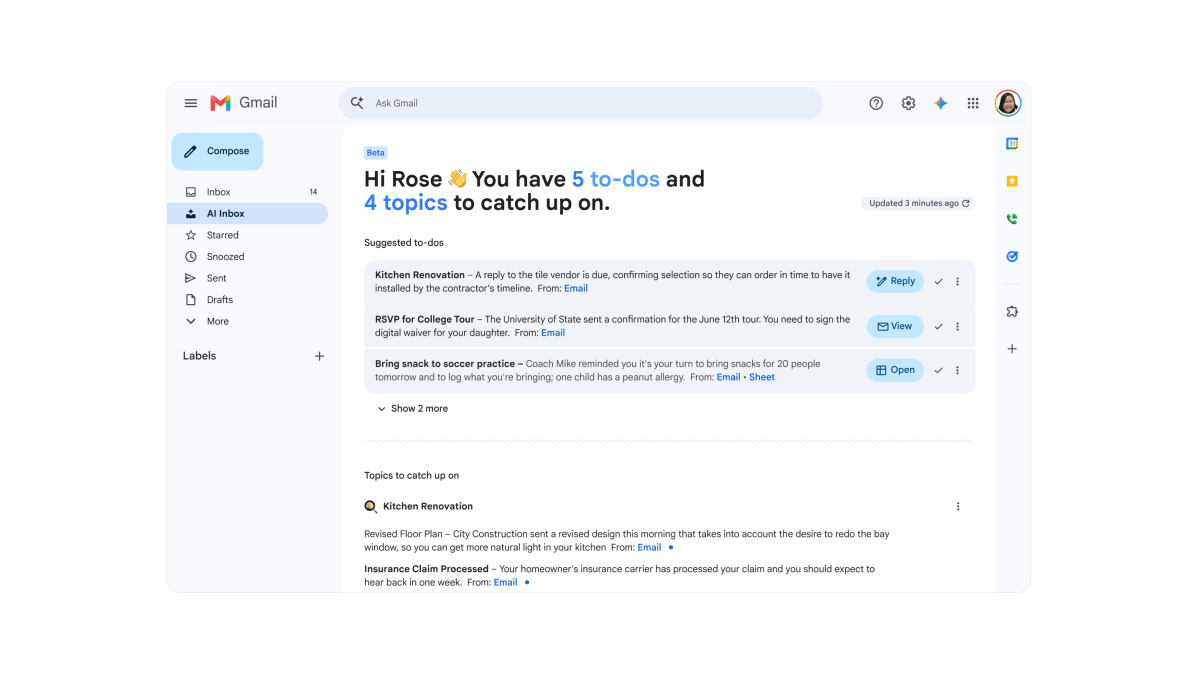
Interested in having AI help you manage your email? If you let Claude, ChatGPT, Gemini, or Meta’s Muse into your Gmail inbox, you can take steps to protect your messages—as well as your privacy.
To do so, you’ll need to dig into the rules or settings for your chosen AI chatbot. If you’re not sure where to find them, use our guide.) In addition to checking over the permissions, you can disallow the models from training on your data.


